Shorter Secure Sockets Layer (SSL) certificate life cycles are impacting certificate management workflows. With the next reduction occurring on March 15, 2027, companies working with multiple providers face more frequent renewals across different systems and processes.
Our 2026 research, published in The SSL Landscape: Six-Month Checkpoint, found that 55.8% of analyzed Forbes Global 2000 companies use three or more certificate providers on their main domain. This fragmentation may complicate coordination across teams and will become a tougher juggling act when certificate life cycles fall from 200 to 100 days this March.
What a fragmented operating picture really looks like
Our research analyzed approximately 246,100 certificates across the core domains of Forbes Global 2000 companies. Only 24.2% of analyzed companies used a single provider on their main domain.
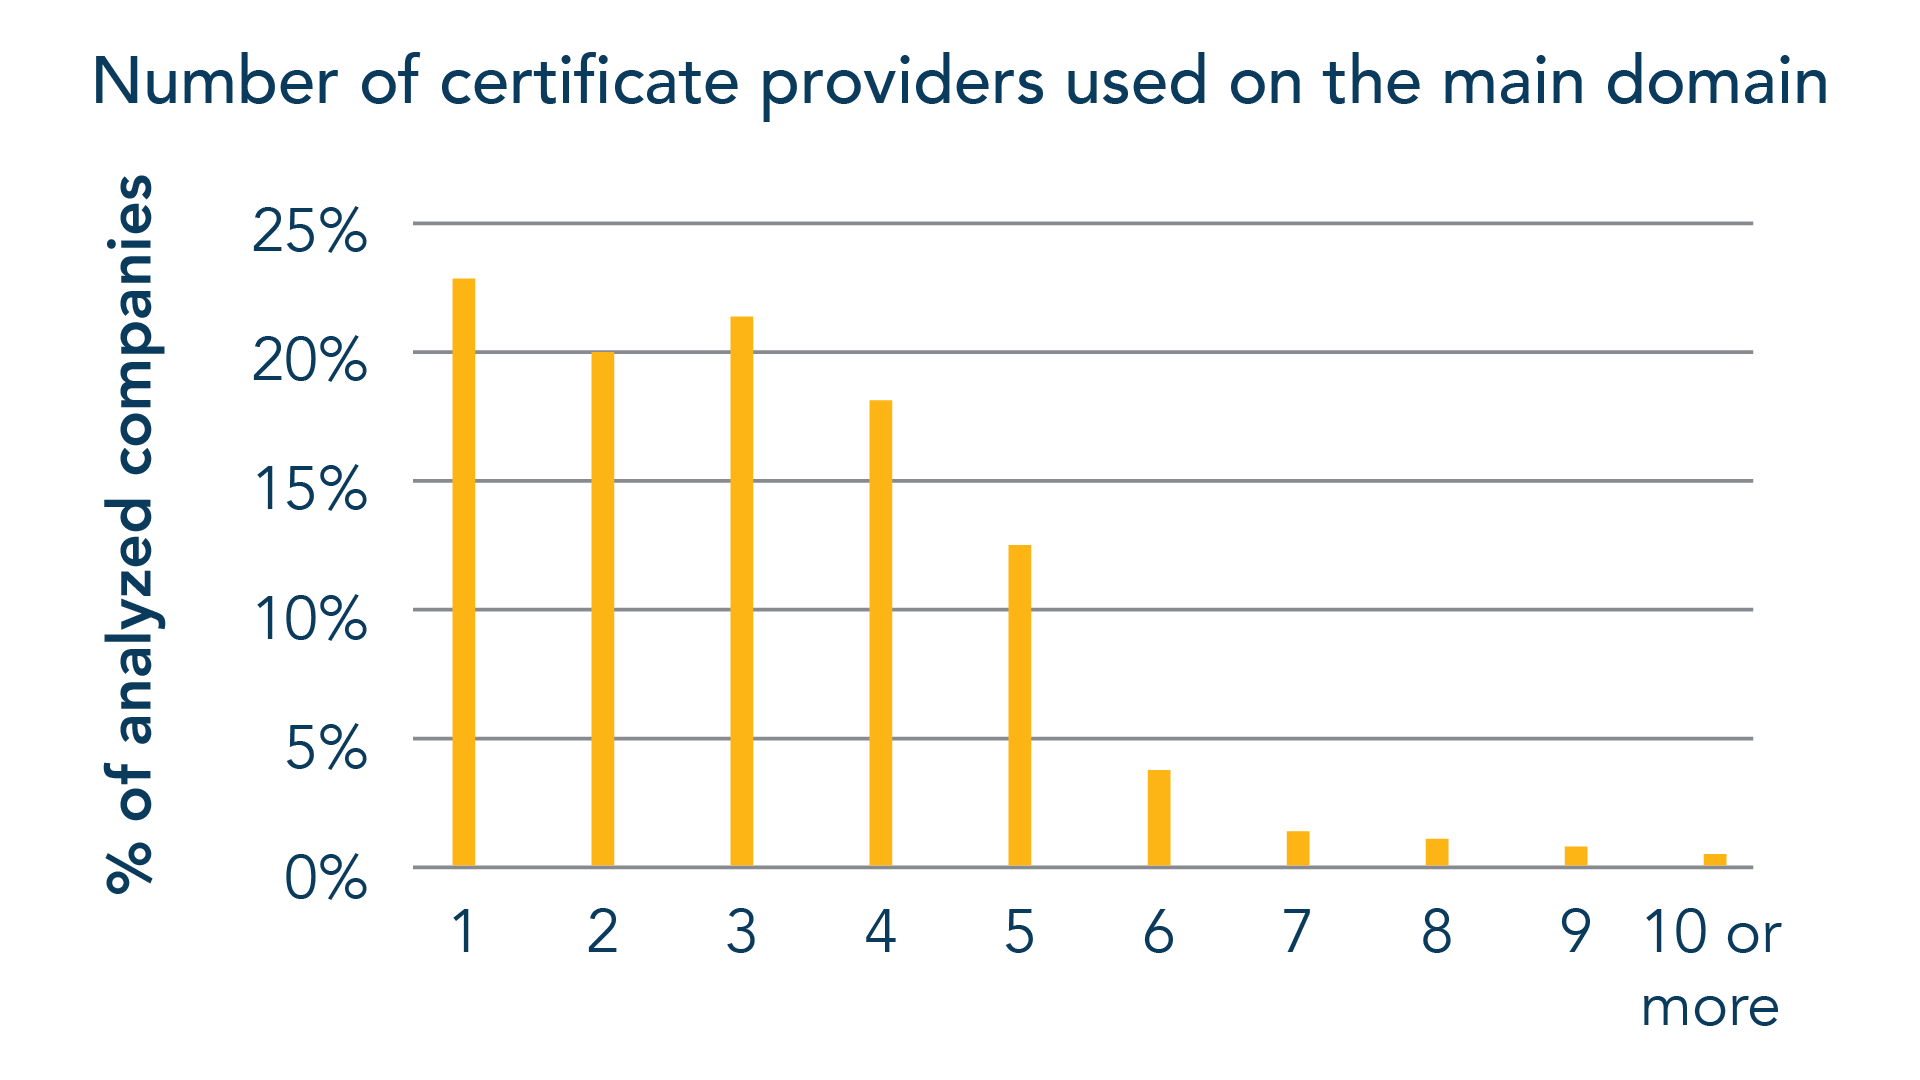
Although the number of providers alone doesn’t establish whether an organization’s environment is insecure, it paints a picture of the fragmented operational reality that teams deal with. They must often contend with scattered inventory, differing renewal timeframes and notices, and inconsistent processes.
In addition, certificates sourced from multiple providers may require teams to manage them across different providers’ portals, respond to renewal notifications in varied formats and schedules, and work with different teams through different channels when troubleshooting. Following a renewal through to completion, therefore, requires additional effort to identify each provider and its separate workflows.
The operational load of multiplied processes
The timetable is already changing. On March 15, 2026, the maximum life cycle for newly issued publicly trusted Transport Layer Security (TLS) certificates fell to 200 days. On March 15, 2027, it will fall again—this time to 100 days.
For certificate operations, the consequence is greater frequency. Shorter life cycles mean that the sequence of issuance, validation, and installation recurs more often, increasing the administrative burden.
Our analysis also found that about 41% of certificates had one-year validity periods. This suggests that some companies may not yet have experienced the full operational impact of shorter-term certificates at the research checkpoint.
Portfolio scale adds to the pressure
Provider fragmentation complicates another major factor: substantial certificate portfolios. Our research revealed that 58.6% of analyzed companies had more than 10 certificates on their main domain, while roughly one in five had more than 100. A few had more than 15,000 each.
Fragmented ownership and processes could become even more difficult to sustain at a larger scale. Missing even one renewal could disrupt applications and websites, with potential consequences for revenue, reputation, and trust.
Together, the findings describe an existing coordination challenge operating on a faster timetable. As the 100-day phase approaches, provider fragmentation becomes increasingly relevant to how frequently teams must manage those interactions across substantial portfolios.
For the full findings, download The SSL Landscape: Six-Month Checkpoint.